Reverse engineering an x86-64 executable
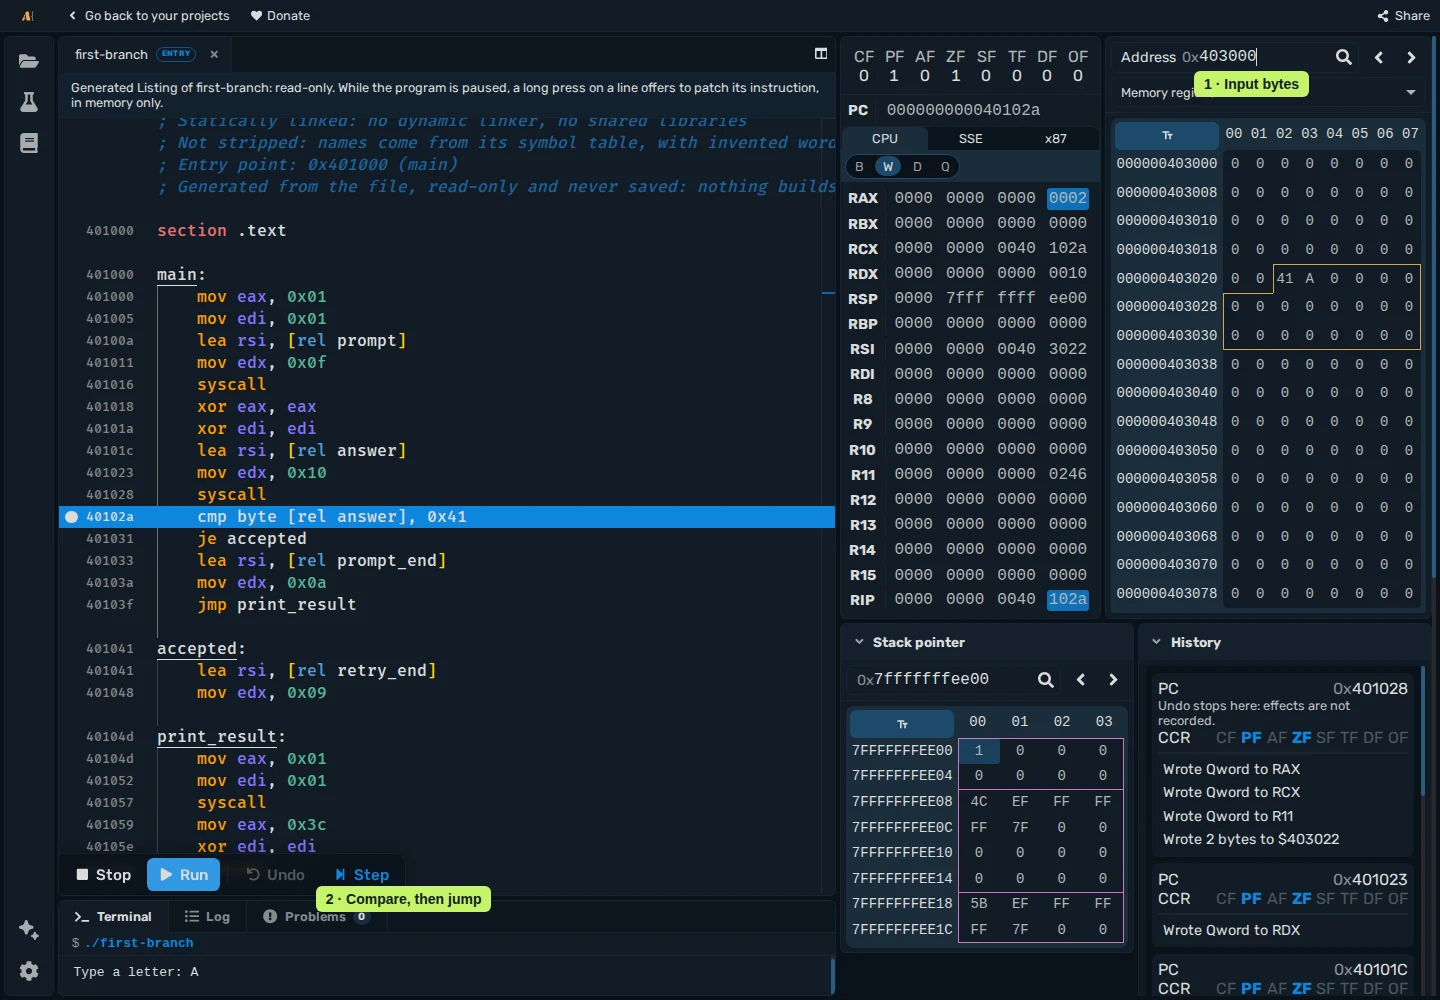
Import a Linux executable and follow an input byte through a comparison, flag, and conditional jump.
Inspect x86-64 executables using disassembly, breakpoints, registers, and memory.
Import a Linux executable and follow an input byte through a comparison, flag, and conditional jump.